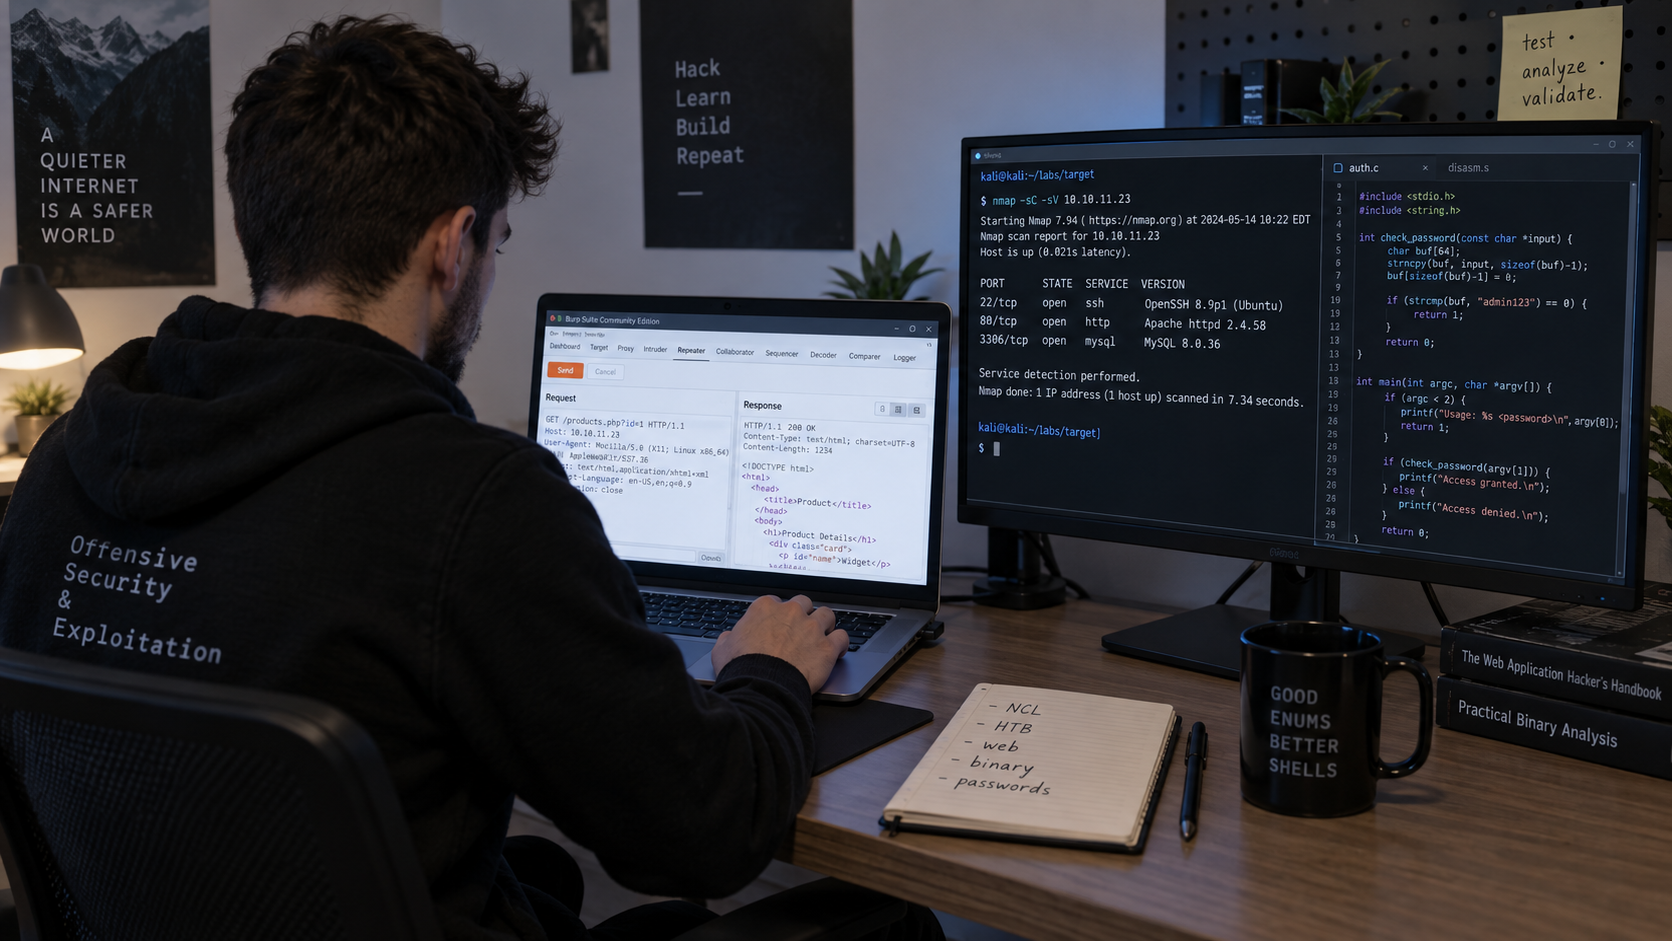
Hands-on offensive security and exploitation.
Performed controlled web application testing, binary exploitation, reverse engineering, password auditing, and system exploitation across NCL and Hack The Box lab environments.
Representative Work: NCL Fall 2026 · Hack The Box
Representative Offensive Work
Web Application Testing
Context: NCL Fall 2026Tested web applications for path traversal, client-side authorization weaknesses, input-type issues, and SQL injection using browser tools and Burp Suite.
Binary Exploitation & Reverse Engineering
Context: NCL Fall 2026Analyzed binaries and validation logic using GDB, pwntools, decompilation, cyclic patterns, stack offsets, bitwise operations, and return-to-function techniques.
Password Auditing
Context: NCL Fall 2026Used John the Ripper and Hashcat with hash identification, structured masks, custom wordlists, hybrid attacks, and rule-based mutations to evaluate password weaknesses.
System Exploitation
Context: Hack The BoxWorked through controlled end-to-end lab scenarios involving reconnaissance, service enumeration, web weaknesses, foothold development, credential discovery, and privilege escalation.
Tools & Skills
Tools & Techniques
Nmap · Burp Suite · GDB · pwntools · Hashcat · John the Ripper · Git · Python · Kali Linux
Skills Demonstrated
Web Application Testing · Enumeration · Binary Exploitation · Reverse Engineering · Password Auditing · Vulnerability Analysis · Privilege Escalation
Outcome: Applied structured offensive-security methods across web, binary, credential, and system-level challenges in controlled lab environments.